 Image 1 of 1
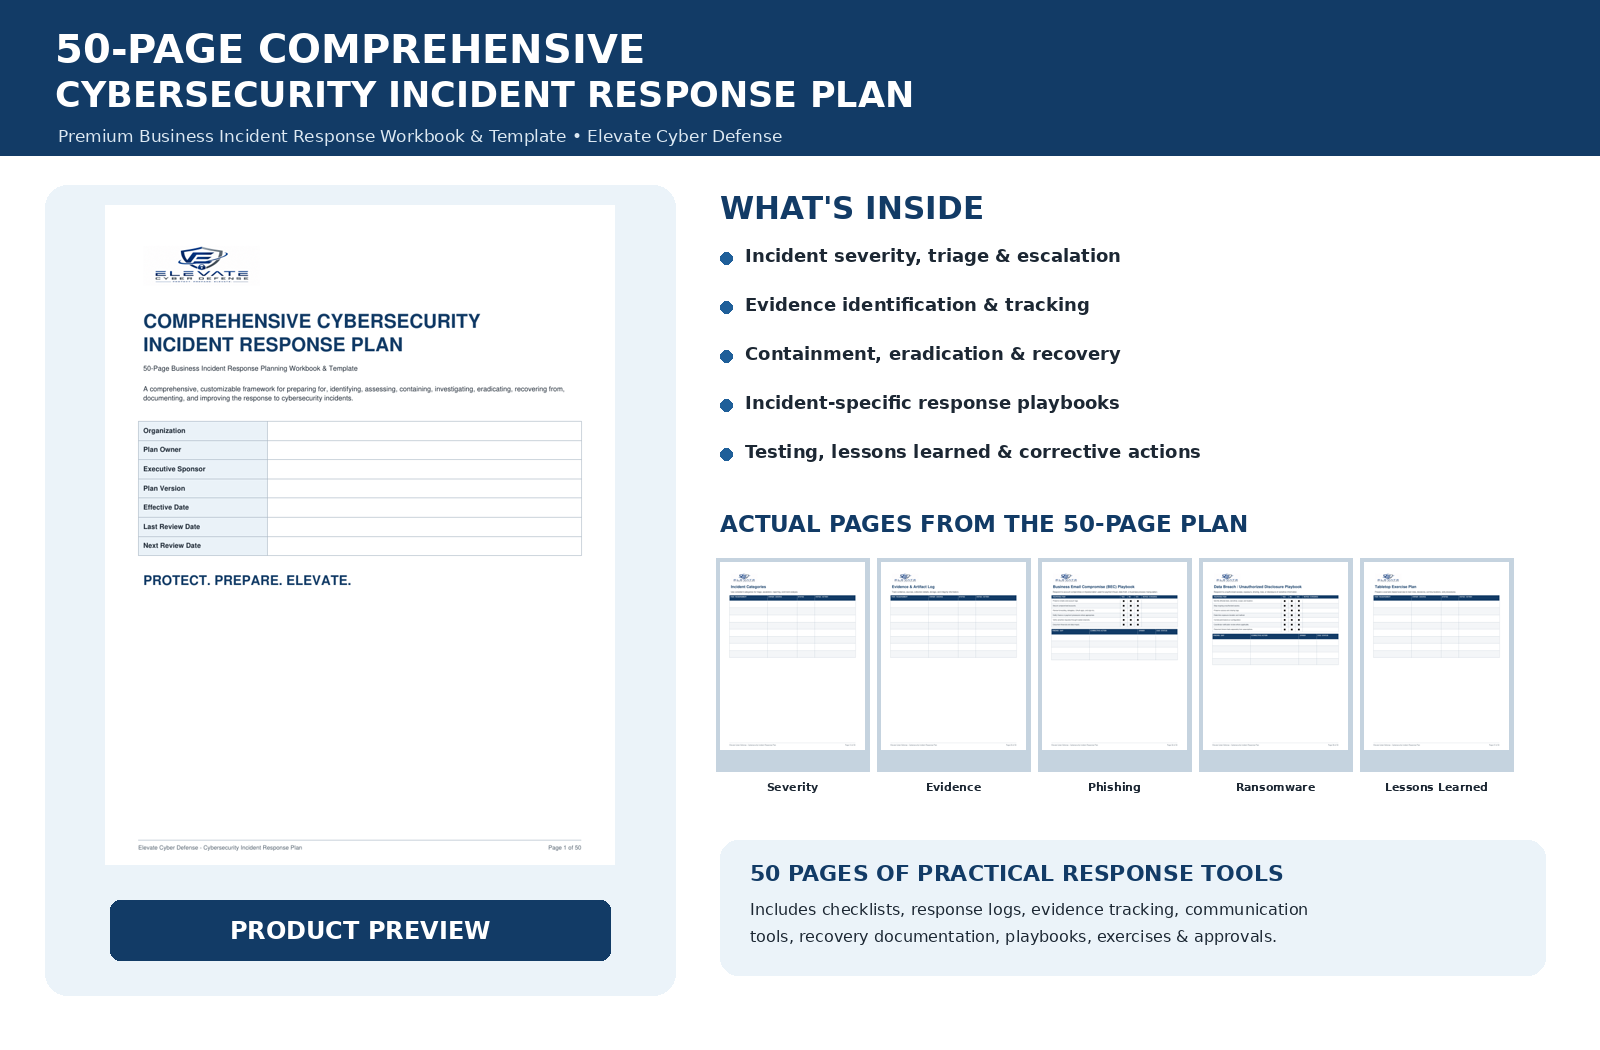
The Elevate Cyber Defense 50-Page Comprehensive Cybersecurity Incident Response Plan provides businesses with a structured, customizable framework for preparing for, identifying, managing, containing, investigating, and recovering from cybersecurity incidents.
Rather than trying to determine what to do during an active security event, this comprehensive plan helps organizations establish roles, responsibilities, escalation procedures, response processes, documentation requirements, communication procedures, and incident-specific response actions before an incident occurs.
Incident response plan governance and document control
Incident response team roles and responsibilities
Emergency contact and escalation information
Cybersecurity incident identification and reporting
Incident intake and initial assessment
Incident classification and severity levels
Incident prioritization and escalation
Response activation procedures
Incident investigation and documentation
Evidence identification and handling
Incident timeline and activity tracking
Incident decision logs
Containment planning and actions
Short-term and long-term containment
Threat eradication procedures
System and account recovery
Recovery validation and monitoring
Internal communication procedures
Employee incident notifications
Customer and stakeholder communication planning
Vendor and third-party coordination
Legal, regulatory, contractual, and insurance notification review
Cybersecurity incident reporting documentation
Phishing incident response
Business Email Compromise (BEC) response
Compromised account and credential response
Malware incident response
Ransomware incident response
Data breach and unauthorized disclosure response
Lost or stolen device response
Insider threat response
Cloud and SaaS security incident response
Network security incident response
Third-party and vendor incident response
Denial-of-service and service disruption response
Incident evidence and artifact tracking
Affected system and account tracking
Incident containment checklist
Incident recovery checklist
Post-incident review
Root-cause analysis
Lessons learned
Corrective-action tracking
Incident response testing and tabletop exercises
Plan maintenance and annual review
Final management review and approval
The plan is designed to give businesses a repeatable incident-response process instead of relying on improvised decisions during a cybersecurity emergency.
The included worksheets, checklists, response procedures, tracking logs, documentation fields, and incident-specific playbooks can be customized to match your organization's technology environment, employees, vendors, operations, and cybersecurity risks.
Ideal for small businesses, growing organizations, IT teams, business owners, and organizations developing or strengthening their cybersecurity preparedness.