 Image 1 of 1
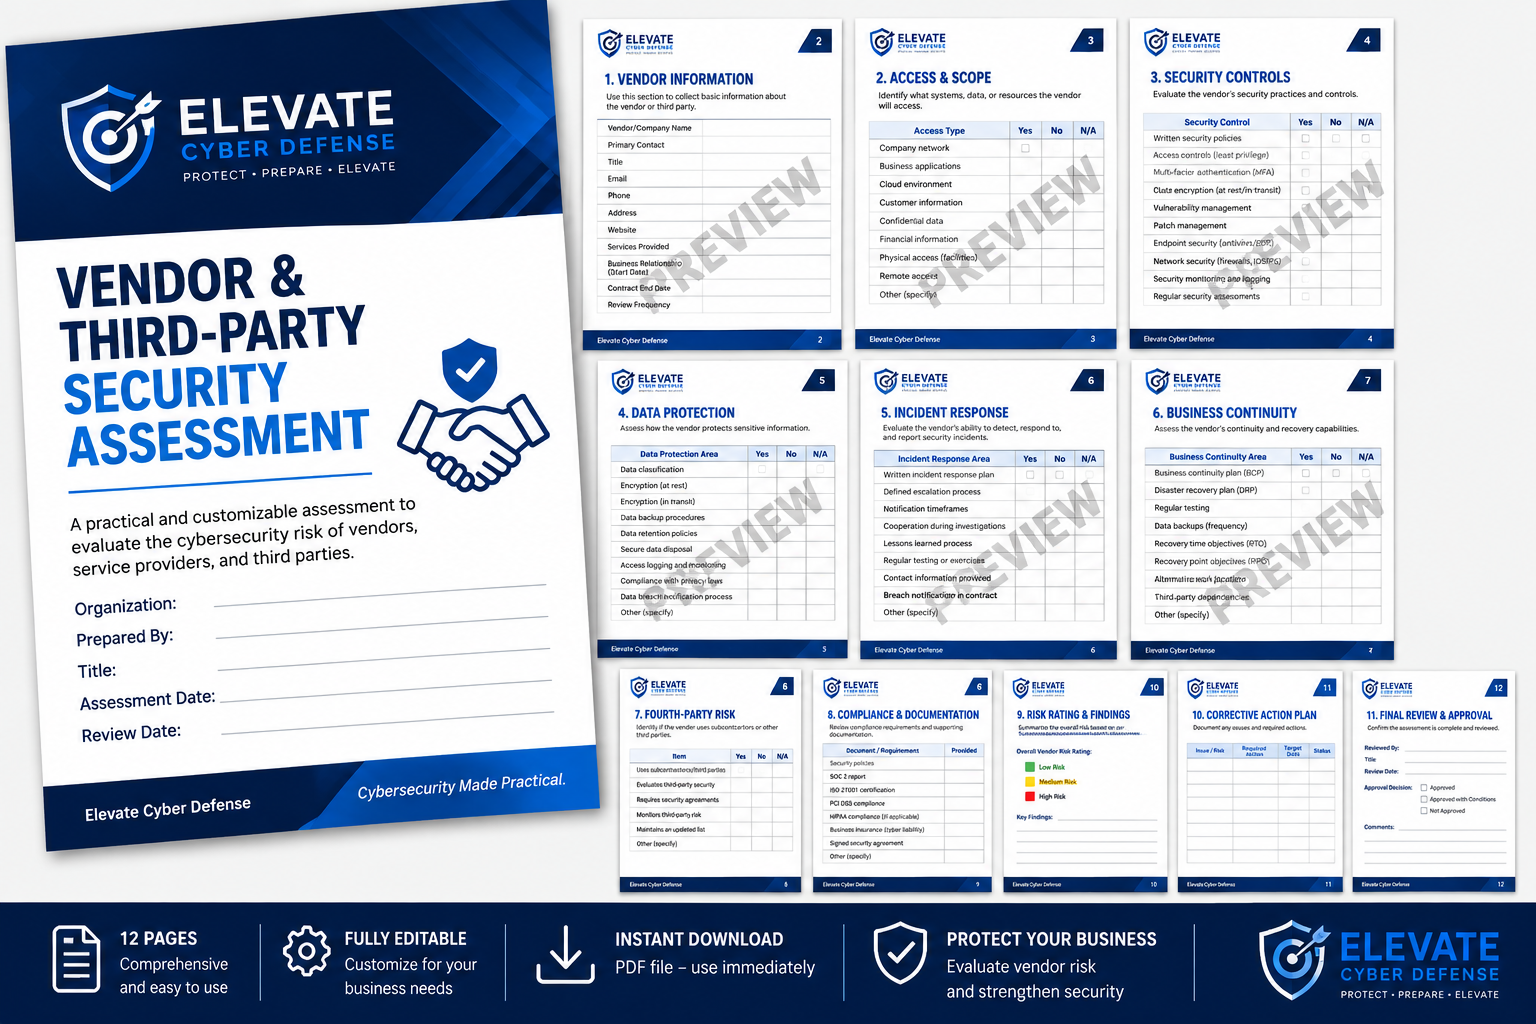
The Vendor & Third-Party Security Assessment provides businesses with a structured third-party vendor security assessment process for evaluating and documenting the cybersecurity practices of vendors, service providers, contractors, and other third parties that may access business systems, networks, applications, or sensitive information.
Third-party relationships can introduce cybersecurity risk when outside organizations have access to company data, customer information, cloud environments, business applications, or critical services. This customizable assessment helps businesses identify potential security concerns, document vendor safeguards, and make more informed decisions before establishing or continuing a third-party relationship.
Use this assessment to evaluate and document:
Vendor and third-party information
Services provided and business relationship
Access to company systems, applications, and networks
Access to sensitive, confidential, or customer information
User access controls and least-privilege practices
Password and multi-factor authentication (MFA) protections
Data protection, encryption, storage, and transmission
Security policies and cybersecurity practices
Vulnerability and patch management
Endpoint and network security
Cybersecurity incident response and notification procedures
Business continuity, disaster recovery, and backup practices
Subcontractor and fourth-party relationships
Security awareness and employee practices
Compliance and supporting documentation
Identified security concerns and required corrective actions
Overall vendor risk rating
Final review, approval, and reassessment requirements
Designed for small and growing businesses, this resource provides a practical framework for evaluating third-party cybersecurity risk before onboarding a new vendor and during periodic reviews of existing vendor relationships.
Best For: Small businesses, business owners, IT teams, managers, security teams, and organizations that rely on vendors, contractors, cloud providers, technology providers, or other third parties.